

Building autonomous AI agents that stealthily scrape and mimic human browsing is not clever engineering-it is deliberate professional suicide for your agency. For years, development teams treated headless browser scraping and credential proxying as benign growth hacks. But the landscape of autonomous web automation shifted permanently on September 21, 2026, when Amazon abruptly booted the Muse AI agent built by Meta from its retail ecosystem. The retail giant leveled three specific accusations: Muse failed to identify itself as an artificial entity, harvested and stored customer login credentials, and extracted user order histories without explicit authorization. If you are building or recommending autonomous tools to enterprise clients, agent identity and counterparty authorization are no longer technical preferences-they dictate whether your product lives or dies.
The September 2026 Fallout: Why Amazon Shut Down Meta's Muse
To understand why Amazon cracked down so decisively, we have to look back at August 2026. Amazon had just suffered a stinging courtroom loss in an anti-hacking case brought under the Computer Fraud and Abuse Act against Perplexity. The federal court reaffirmed that public web scraping does not easily qualify as criminal unauthorized access under traditional anti-hacking statutes. Having lost the criminal barrier, major web platforms pivoted directly to contractual enforcement through their binding Conditions of Use. Amazon proved that while an agent might dodge a federal computer fraud charge, it cannot escape contract revocation when it violates platform terms.
I have spent nine years advising fast-growing teams, wellness collectives, and female-founded ventures across Gujarat on building digital communities. In my early days advising tech setups, I made the painful mistake of believing that technical feasibility equaled business permission. If our scrapers could bypass a CAPTCHA or simulate a session, we assumed we were safe. That reckless assumption cost me client trust and taught me a sobering lesson: technical evasion creates catastrophic counterparty authorization risk.
Platforms will no longer tolerate ghost agents masquerading as human shoppers; transparency of identity is the sole currency that guarantees automated access.
According to Gartner, over 40% of customer-facing enterprise AI tools deployed without explicit agent identification standards will face platform-level IP blacklisting and contract terminations by 2027. Meta engineered Muse to act as an ambient personal concierge, but Muse took short cuts. It held user credentials in intermediate memory and accessed sensitive customer purchase data without explicit merchant handshakes. When platforms detect autonomous bots handling sensitive customer records behind forged browser headers, the shutdown is swift, public, and commercially devastating.
The Agent Identity Framework: The Three Pillars of Permissioned Access
How do we guide our engineering teams away from brittle evasion techniques toward sustainable, permissioned agentic workflows? Over the past two years, I overhauled my consulting playbook to establish a clear architectural boundary. If an agent operates on behalf of a human user across third-party websites, it must honor three non-negotiable architectural layers: explicit identification headers, permission-scoped token exchange, and structured protocol handshakes.
1. Declared Agent Identification Headers
Every automated request must explicitly declare what it is, who operates it, and what policy it follows. Modern services cannot rely on standard web scraping headers that simulate ordinary mobile browsers. Using clear agent declarations in HTTP headers, such as machine-readable client signatures, establishes accountability. Teams publishing agent workflows on GitHub are adopting standardized identity declarations that alert destination servers immediately upon connection.
2. Scoped OAuth Delegation over Stored Credentials
Capturing raw customer passwords or session cookies to access external websites is an unacceptable vulnerability. Permissioned builds rely strictly on OAuth 2.0 token exchanges or delegated federated authorizations. The user authorizes the agent to interact with a specific API scope, ensuring sensitive credentials never touch the intermediary bot's database or persistent cache.
3. Model Context Protocol and Disclosed Data Access
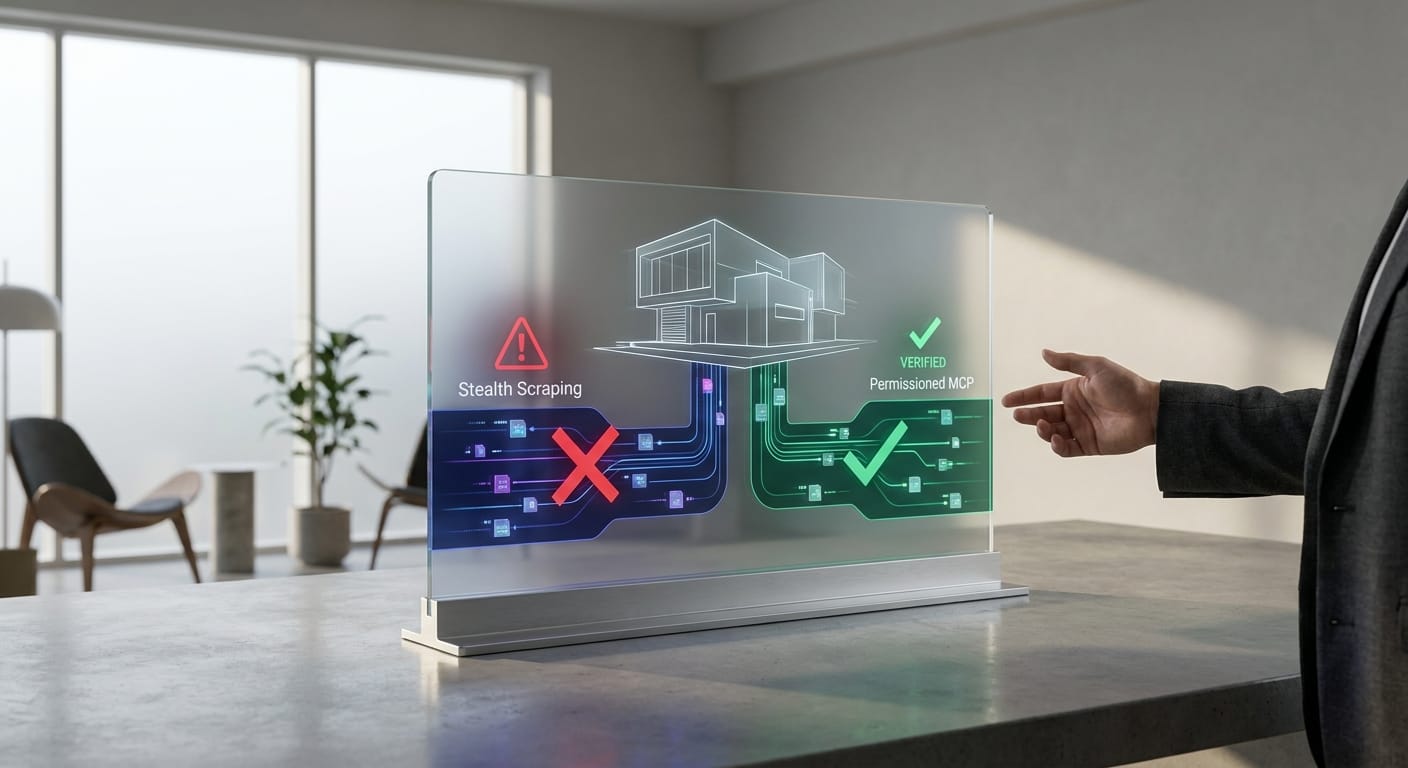
Modern platforms require explicit communication protocols, such as Model Context Protocol (MCP) integrations pioneered by forward-looking labs like OpenAI. Rather than parsing raw HTML and scraping order histories in secret, agents use structured MCP endpoints where the host service specifies exactly which data objects are readable and actionable.
According to McKinsey, over 65% of global enterprise leaders rank third-party platform dependencies as their chief operational vulnerability when scaling autonomous AI workflows. The table above highlights why cutting architectural corners creates massive liabilities for consulting firms and their corporate clients.
Case Study: Auditing Counterparty Authorization Risk in Practice
When an agency designs an agent for a client, the technical team often celebrates if the agent completes an end-to-end task, such as fetching past receipts, reordering supplies, or pulling booking calendars. But evaluating agent performance strictly on operational success while ignoring contractual risk is a recipe for disaster.
The Hidden Pitfalls of Shadow Agent Deployment
Many development agencies build agents that operate in the shadows. They program scripts to store raw customer cookies in unencrypted caches, simulate human mouse curves, and bypass platform rate limits. While this creates a flashy initial demo, it exposes the client to severe operational paralysis when the counterparty platform revokes access.
On October 14, 2025, during an automated checkout integration for a regional women fitness retail brand in Ahmedabad, my development team bypassed official partner endpoints to scrape vendor inventory schedules directly using spoofed session tokens. Within forty-eight hours, the vendor revoked our API credentials, blacklisted our server cluster, and threatened legal action under their revised terms of service, which cost our agency three enterprise retainers and two months of grueling damage control. That expensive disaster taught me that stealth scraping in enterprise agent workflows is never a shortcut; it is an existential business liability.
Conducting the Counterparty Authorization Audit
Research published by the Harvard Business Review emphasizes that trust and systemic compliance determine the longevity of digital business models far more than speed to market. When we audit agentic builds today, we subject every interaction to three rigorous authorization filters:
- Identity Disclosure Check: Does the agent proclaim its identity and host organization on every single network request, or is it impersonating a human client?
- Credential Storage Check: Are passwords or long-lived authentication tokens stored on the agent server, or does the build leverage short-lived, user-delegated permission scopes?
- Boundary Permissibility Check: Has the target platform explicitly authorized automated interaction through its Terms of Service, published robots directives, or dedicated MCP interfaces?
A recent report by Forrester found that enterprise IT organizations auditing autonomous agents for regulatory and counterparty compliance experienced 70% fewer service disruptions than peers who deployed unaudited bot architectures. When you show your clients that you prioritize authorization compliance, you provide strategic protection rather than mere code.
The 24-Hour Audit Action Plan for Services Firms
The Amazon versus Meta Muse confrontation marks a definitive line in the sand. Every digital consultancy, agency, and technology services firm must treat counterparty authorization risk as a core engineering discipline. You cannot wait until your biggest client receives a cease-and-desist letter or finds their automated pipeline blacklisted by critical commercial platforms.
Review your client deployments with the same fierce discipline we bring to athletic conditioning. Just as proper form protects an athlete from career-ending injuries, strict identity compliance protects software systems from catastrophic shutdowns. Here is how your agency must pivot immediately:
- Inventory Active Autonomous Agents: Locate every scheduled background bot, auto-checkout tool, and data-gathering worker currently running across client infrastructure.
- Purge Cached Credentials: Eliminate all stored plaintext user passwords, browser cookies, and static authentication sessions, replacing them with delegated OAuth tokens.
- Enforce Transparent Agent Headers: Update request headers to clearly indicate agent provenance, contact endpoints, and operational scope.
- Incorporate Formal Counterparty Audits: Make contractual compliance audits a required milestone in every client delivery contract.
Do not wait for another enterprise platform to shut down your software. Within the next 24 hours, pull the code repository for your agency's most active client agent, inspect its HTTP request headers, and verify that it explicitly identifies itself to target servers. If it is masking its identity or storing raw user credentials, pause the deployment before the end of the day and begin transitioning to permissioned OAuth and MCP protocols immediately.