

Nearly seventy-two percent of enterprise application deployments assisted by artificial intelligence encounter severe procurement and compliance delays before ever reaching commercial production. If your organization relies on vendor promises of automated velocity, this statistical barrier threatens your operational balance sheet and your digital compliance posture. Three years ago, while advising on cross-border technical compliance from Dublin, I made the costly error of prioritizing lines of code generated per developer day over verifiable provenance. I encouraged partners to celebrate high throughput, only to watch a multi-million-euro financial services contract collapse under scrutiny from European Union regulators because no engineer could trace why a black-box automated algorithm modified critical transactional logic. That failure forced me to recognize that velocity without verification is merely compounding technical debt.
The Procurement Reckoning: How Enterprise Application Services Outgrew Raw Speed
On September 24, 2026, Information Services Group published its landmark Provider Lens study evaluating AI ADM services across fifty-nine global vendors, officially designating twelve industry leaders including Tata Consultancy Services, Infosys, and Accenture. While trade commentators reflexively fixated on vendor ranking tiers, the analytical heart of the report articulated a fundamental transformation: enterprise application services in the United States and Europe have ceased to function as mere delivery capacity engines. Corporate procurement boards are no longer purchasing developer hours or unvalidated generation benchmarks, demanding instead trusted software intelligence where every automated change is documented, mathematically verified, and tied directly to quantifiable commercial returns.
This structural recalibration reflects a convergence between transatlantic procurement rigor and emerging supranational governance frameworks. In the European internal market, directives such as the Digital Operational Resilience Act and the European Union Artificial Intelligence Act have turned algorithmic accountability into enforceable trade policy. Enterprise clients subject to strict supply-chain due diligence cannot permit unverified autonomous scripts to alter production environments without establishing evidentiary paper trails. Consequently, North American enterprises trading across European economic corridors have quietly discarded the vanity metrics of synthetic code throughput in favor of auditable integrity.
The era of the frictionless vendor pitch boasting algorithmic productivity multipliers has met its inevitable demise within corporate legal departments. Procurement officers who once approved digital transformation initiatives on speculative efficiency arguments now mandate forensic traceability across the software lifecycle. If an external service partner claims forty percent efficiency gains via machine intelligence, procurement demands explicit documentation detailing which developer reviewed the prompt, how the syntax aligns with regulatory data governance, and what exact business metric improved. Providers incapable of satisfying this evidentiary mandate are systematically eliminated from tier-one consideration.
The Trust Architecture: Why Audit Trails Trump Raw Scale
To navigate this emerging landscape, technology leaders must dismantle the false assumption that scale determines dominance in automated software engineering. The operational moat in modern application development and maintenance no longer resides in training proprietary foundational models or acquiring massive pools of offshore labor. As demonstrated by recent research from McKinsey, generative capability has become commoditized across consumer and enterprise tooling alike. The enduring competitive moat is now the evidence layer: the comprehensive, immutable framework that captures the intent, review history, and economic outcome of every altered system state.
Mid-sized system integrators and specialized consultancies can decisively outperform legacy global providers within this transformed paradigm. Establishing rigorous audit trails is fundamentally a deterministic process problem rather than a scale problem. Large systems integrators frequently struggle with fragmented global delivery units, discordant documentation repositories, and legacy margin incentives built upon billing billable headcounts. In contrast, agile mid-market firms can enforce strict provenance standards, embed automated policy validation directly into version control pipelines via GitHub, and deliver verifiable governance at a fraction of bureaucratic overhead.
Enterprise procurement departments have realized that an unverified algorithmic commit is an unquantifiable legal liability, converting pure delivery speed into an organizational vulnerability.
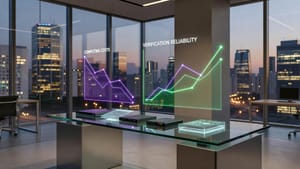
According to comparative industry findings compiled by Gartner and corroborated by Forrester in their 2025 technology market analyses, organizations that prioritize governance frameworks over algorithmic speed realize superior economic resiliency. The table below illustrates the shift in operational priorities separating legacy throughput from an evidence-first delivery framework.
Constructing the Tripartite Verification Triad
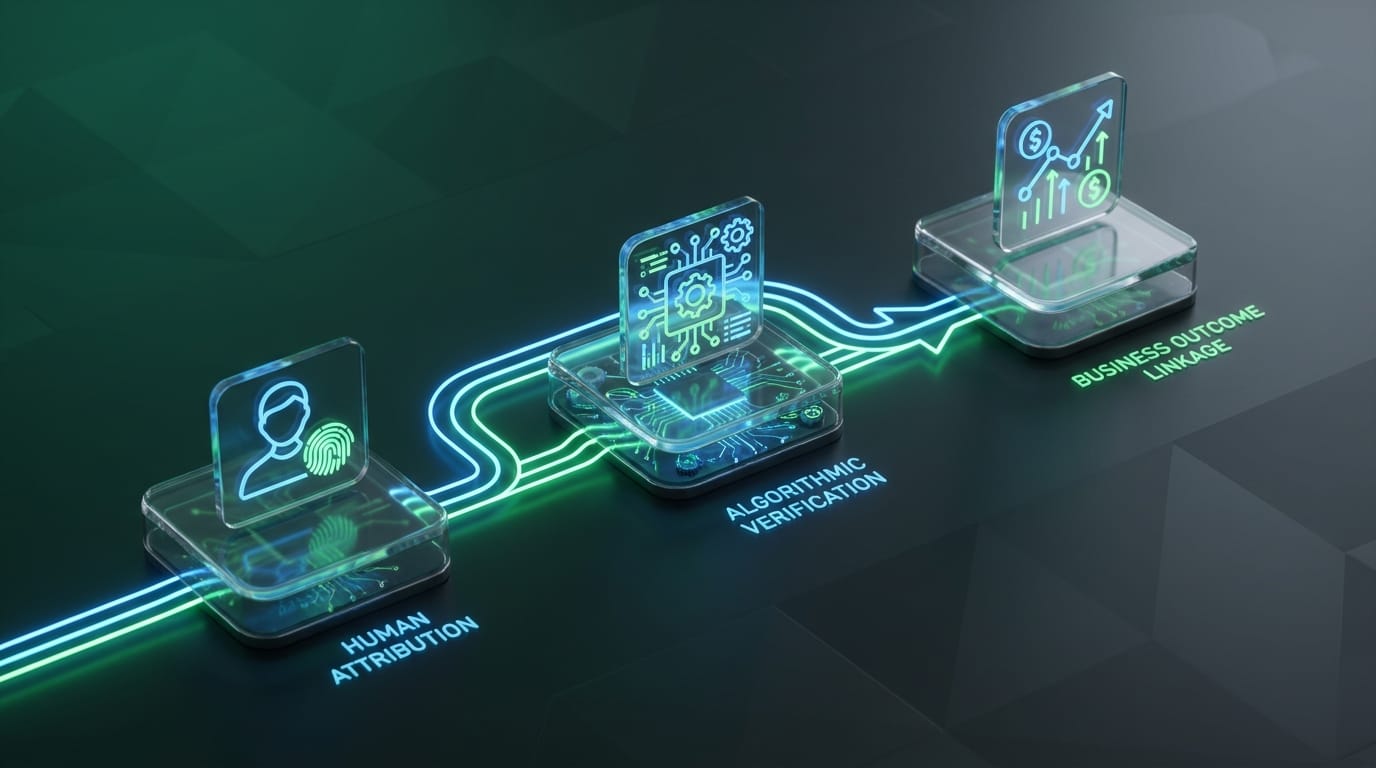
An authentic evidence architecture rests upon three mandatory pillars: human attribution, algorithmic verification, and outcome linkage. Human attribution guarantees that an identifiable senior engineer assumes legal responsibility for every machine-synthesized commit, directly mirroring professional liability concepts prevalent under European civil law. Algorithmic verification subjects changes to deterministic testing batteries to ensure software behavior aligns strictly with published security guidelines. Finally, outcome linkage establishes a documented causal relationship between code refactoring and specific organizational key performance indicators.
Inside the Audit Crucible: How Mid-Market Agility Defeated Legacy Monoliths
Consider the recent case of an international logistics consortium operating across Antwerp, Rotterdam, and Dublin that issued a tender to modernize its customs clearance architecture. A premier global consultancy submitted an aggressive proposal centered on high-volume automation, utilizing integrated models from IBM and code assistance frameworks provided by Microsoft. Their proposal promised a sixty percent reduction in development cycle times, yet failed to explain how the resulting microservices would comply with emerging European Union carbon-border adjustment mechanisms and digital reporting requirements.
Simultaneously, a mid-tier regional software engineering firm structured its bid entirely around an auditable evidence framework. Rather than emphasizing raw generation volume, they integrated tracing protocols that connected every algorithmic proposal to compliance standards and business rules. Automated tooling checked logic against trade mandates before generating permanent audit ledgers. As noted in insights published by the Harvard Business Review, enterprise procurement committees are systematically punishing unverified algorithmic risk in favor of operational transparency.
When the logistics consortium's risk evaluation panel examined both proposals, the outcome was immediate and definitive. The incumbent mega-vendor could not demonstrate how synthetic pull requests generated through third-party models from OpenAI would be audited without costly manual intervention. The mid-sized firm secured the thirty-five-million-euro modernization engagement despite quoting twenty percent fewer total developers, proving that procurement officers will pay a premium for verified truth while penalizing speculative automation claims.
Your 24-Hour Mandate: Dismantling Unprovable AI in Your Pipeline
Surviving this market realignment requires immediate, surgical intervention in your commercial and technical workflows. Application leaders cannot afford another quarter of unsubstantiated vendor assurances or internally unmonitored code generation. The market has permanently shifted from delivery capacity to trusted software intelligence, and your organization must adjust its operational baseline accordingly.
Begin by identifying every artificial intelligence tool currently deployed across your development teams or supplier contracts. Establish whether each automated suggestion leaves an immutable audit trail detailing prompt parameters, technical reviewer identity, and associated unit-test coverage. If an existing vendor cannot supply documentary evidence verifying their code generation claims within your current pipeline, freeze their discretionary expansion until their evidentiary process satisfies institutional procurement standards.
Take this concrete step within the next twenty-four hours: pull the last three pull requests committed to your critical core repository by external service vendors, and demand an auditable lineage report identifying the exact human reviewer, the verification battery applied, and the verified business requirement linked to each change. If your vendor cannot deliver that forensic proof before tomorrow's close of business, invoke your contract's audit clause and halt billing on those deliverables immediately.